Jamf Mobile Forensics
If you suspect a phone in your company has been compromised, we deploy Jamf Mobile Forensics and look for signs of an attack on the device together with your security team.
This fits if you...
Have an Apple threat notification or suspicious activity on a phone to investigate
Look after executives and other people whose phones hold sensitive business information
Want findings your security team can use to decide what happens next
How we run an investigation
Your security team sets the scope with us before we start, and stays involved at every step.
We review the concern with you, check that the devices meet the requirements and list the access we'll need.
We set out how diagnostic data is collected and how it's handled afterwards.
We deploy and configure Jamf Mobile Forensics on the devices in scope.
We go through the findings with your team, including what they can't tell you, and plan the next steps of the response.
Your security team has to decide what happens to a phone that may have been compromised, and it needs evidence to do that. Sometimes nothing has happened yet, but the phone holds sensitive business information and you want to know where you stand.
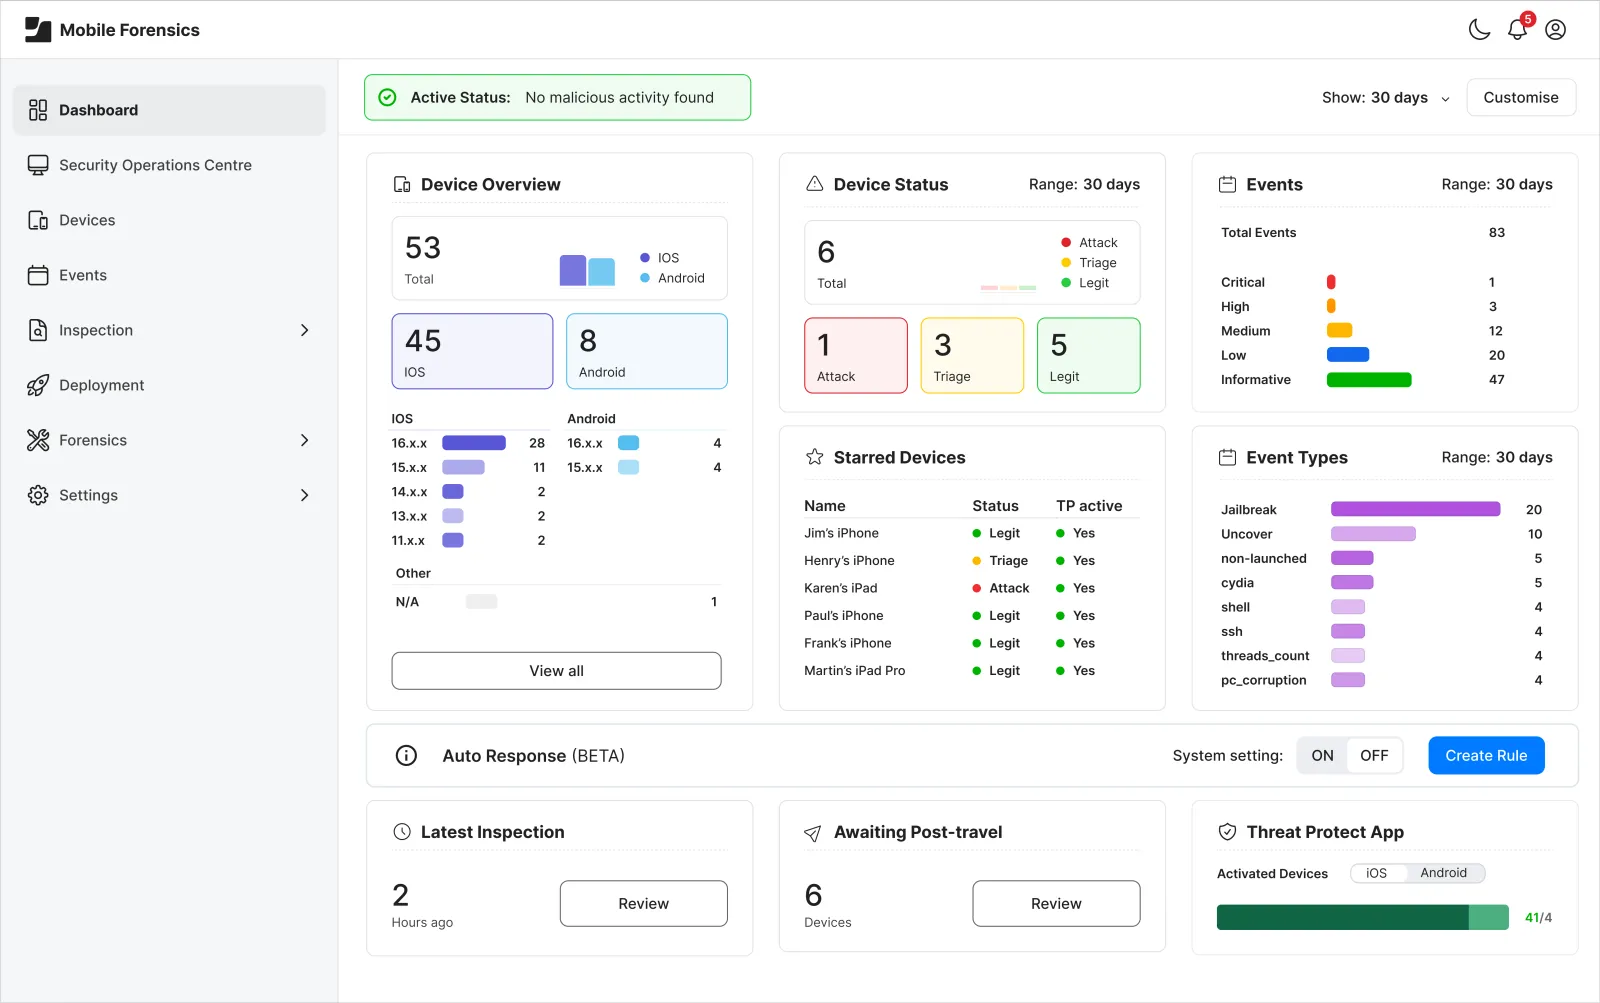
Jamf Mobile Forensics analyses diagnostic telemetry from iPhones, iPads and Android devices for signs of sophisticated attacks. When it flags something, we work out with your security team what it means and plan the response.
After a threat notification from Apple
Apple doesn't say what triggered a threat notification. We help you assess the situation and look on the phone for possible signs of compromise.
Before and after a trip
We can check a phone before someone travels and again when they're back, and compare the two results. If something suspicious shows up, we look into it before the phone connects to sensitive systems again.
Evidence your security team can use
Jamf Mobile Forensics collects system logs, kernel logs and crash reports from the device and analyses them automatically. Your team can use the results in an incident investigation. The threat research and detection data behind the analysis come from Jamf Threat Labs.
Features
Forensic analysis of iPhone, iPad and Android devices
Looks for known vulnerabilities and suspicious behaviour
Investigates devices remotely
Collects diagnostic data automatically
Works on company-owned and personal devices
Our credentials for this platform
 Jamf Partner ProfessionalJamf
 Jamf Pro
Certified ExpertJamf Jamf Pro
Certified AdminJamf Jamf Pro
Certified AssociateJamf Security ConsultantJamf
 Jamf Pro
Certified TechJamf Management ConsultantJamf
 Management IntegratorJamf
 Management EngineerJamf
 AmbassadorJamf
 EducatorJamf
 Security Engineer | MobileJamf
 Jamf Protect
Certified AdminJamf Jamf Protect
Certified AssociateJamf
Useful links
Questions about Jamf Mobile Forensics
Tell us which phones worry you and why. We'll plan the investigation with you.
Tell us what you use today, and we'll say which tool fits and what setting it up would involve. The call costs nothing and takes half an hour.
Related services
- Plan security & complianceCheck your Macs, iPhones and iPads against your security rules and get evidence your security team and auditors can use.
- Investigate targeted attacksCheck a phone for signs of a targeted attack after an Apple threat notification or suspicious activity, and plan what comes next with your security team.
